How to Set up a Shared Drive That Stays Organized as Your Team GrowsHow to Set up a Shared Drive That Stays Organized as Your Team Grows

| 0 Comment |

When a business still has just five people, everyone knows exactly where every file is. However, once it grows to 25 or 50 employees, things change. Suddenly, no one is sure whether the proposal they’re working on is still the latest version or whether a contractor still has access to last year’s project. The shared drive now contains three subfolders, all titled “Final.”

Most business cloud storage tools provide the basics, but they won’t organize themselves. The goal is to keep the shared drive manageable as more people and files are added, without creating extra work for anyone handling day-to-day operations. A useful system makes it easy to find files, keeps access under control, and aligns with the team’s current workflow.

This guide covers how to:

  • Give each file a clear home,
  • Determine who needs access and set the appropriate permissions,
  • Keep files, folders, and access up to date as the team grows.

What is a shared drive?

A shared drive is a central location where teams can store and work on files. Instead of sending attachments back and forth, team members access the same documents and folders, with permissions that determine who can view or edit them.

For growing businesses, this provides a consistent space for collaborative work. Colleagues know where to find the latest proposals, which templates to use, and where to save project files.

How to set up a shared drive

Keeping a shared drive organized means answering three questions: Where should each file be stored? Who needs access? Who is responsible for keeping it up to date?

1. Give each file a clear place

Start from one area that the team uses every day. There is no need to rearrange the entire drive before improving the way the current work is stored.

Choose a few main folders based on your business work. For example:

  • Company resources: Policies, orientation guidelines, and approved templates
  • Operational: Suppliers, procedures, and internal planning
  • Client: Customer work and project files
  • Finance: Budget, invoice, and financial records
  • HR: Employment documents and personnel records

Use subfolders to make files easier to find in each main folder. Inside the Client, create a subfolder for each customer, with a separate project folder in it. In Finance, create a subfolder for each year, with the Invoice and Budget folders separate in it.

For similar projects, reuse the same subfolder name, such as Summary, Work Files, approved work, and client handover. A consistent label helps co-workers understand every new project. If the folder follows the order, add the number so that the order is kept as if sorted by name.

Give a clear name file that tells colleagues about the contents. For monthly reports, include months and years, such as “October 2026 sales report”. For documents that are routinely updated by the team, share the link to one work file for everyone to use the same version.

Tips for applying structure

  • Check sensitive files before thorough cleaning. Review access to financial records and personnel as well as personal client files, then remove permissions that are no longer needed before rearranging less sensitive material.
  • Test the structure on one active project. Ask two co-workers to find a summary, keep drafts, and look for approved jobs. Adjust the labels that they think are confusing.
  • Move the current file first. Check the permissions before and after moving them, update the link in the project tool, and let them know the co-work where the new work should be kept.
  • Handle old files in an easy-to-manage group. Leave it in place when reviewing. Set aside 30 minutes each week, starting from competing versions and hard-to-find files.

2. Determine who needs access

Give people access only to the files they need for their work. Limit access reduces how much information is exposed if the account is compromised and makes permission more manageable when the team changes.

Group files together when they need to be shared with the same person. The company’s policies should be placed in folders that everyone can read, while financial records and personnel require limited access. For client work, separate the files to be submitted from internal drafts and price discussions.

In each folder, give it to the edit to the person who needs to change the file and access to those who just need to read it:

Invite collaborators to remain via email so that you can change or delete everyone’s access separately. When sending the final file to the client, use the sharing link with the expiration date so that access ends when it is no longer needed. Add a password for sensitive files.

Tips to keep the shared files safe

  • Plan access for new employees. Agree which folders people usually need in each role, so you don’t have to decide from scratch every time someone joins. Check our onboarding checklist for more ideas on how to simplify this process.
  • Use an individual account. Each employee must have his or her own account to log in so that you can delete her access without interfering with co-workers.
  • Require two-factor authentication. Proton business administrators can implement it through the organization’s security settings.
  • Treat encryption and permission as separate protection. Proton Drive encrypts the contents of the file, file name, and folder name before leaving your device, thus protecting that information from the storage provider. You still determine which external colleagues and recipients can access the file.

3. Keep the system up-to-date

Show one person as responsible for each main folder to keep the folder useful. The presence of people who can be contacted helps colleagues resolve questions about archiving, mark out expired documents, and ask for access as the team changes.

The document “Start here” that briefly gives the person a place to explain what is included in the folder and how the file should be named. Include this document in on-boarding so that new colleagues understand the system without having to ask to and fro.

The closure of the project is the right time to tidy up. The folder in charge must confirm which files are approved, delete unnecessary duplicates, and move the completed work to the Archive sub-folder with the same access restrictions. Your business retention requirements should be a guide to determining what is stored and what is removed.

Access also needs to be considered when responsibilities change. Include a review of permissions when someone joins, switch roles, or exits, and when the project ends, so that former colleagues and contractors no longer have unnecessary access.

Tips to keep maintenance easy to manage

  • Show backup contacts. Make sure others know the filing rules and how to handle access requests when the folder in charge is non-existent.
  • Set aside time for a short monthly check. Check the resources shared and outdated, old delivery links, as well as unnecessary access, ranging from sensitive folders and external recipients.
  • Plan the handover of the file before deleting the account. Identify the business files that employees have that will exit and store them in the company-controlled storage. Make sure your colleagues can access the saved files before deleting your account. Download our offboarding checklist if you need a simple framework for the employee exit process.

Let the shared drive grow as work

An easy-to-manageable shared drive clarifies where the file is supposed to be stored, who needs access, and who keeps it up-to-date. Use this checklist when setting up the structure and maintaining it as your team evolves:

  • Start from a small scale: Choose one area that your team uses every day and tidy up the current files before handling the material for longer.
  • Give a clear place file: Use the main folder that reflects your work, a consistent subfolder, and a descriptive file name.
  • Control access: Share only what people need, differentiate access from editing access, and set expiration dates for temporary links.
  • Set a responsibility: Design a contact for each main folder and record the filing rules in a short “Start here” document.
  • Keep it up-to-date: Archive the completed work and review the access when the project ends or people change roles or exits.

6 Smart Methods for Document Management6 Smart Methods for Document Management

| 0 Comment |

When you run a business, documents pile up quickly. Contracts, employee records, and commercially sensitive client data tend to accumulate haphazardly unless you have a clear document management system in place.

Digital disorganization poses real risks. Not only does it waste time when you need to find what you’re looking for later, but it can also lead to operational errors or even security breaches.

When the wrong version of a document is circulated, agreements may be executed under incorrect terms, and sensitive information may be inadvertently disclosed. These issues stem from poor document management and result in compliance problems and eroded trust.

Document management isn’t just about keeping files organized; it’s about maintaining control. It helps ensure that the right information is reliable, restricts unnecessary access to sensitive data, and provides visibility into who can view, edit, or share business data.

In this guide, you’ll learn:

  1. What is documentation management?
  2. Why businesses need a method for managing documents
  3. 6 best practices for document management

1. What is document management?

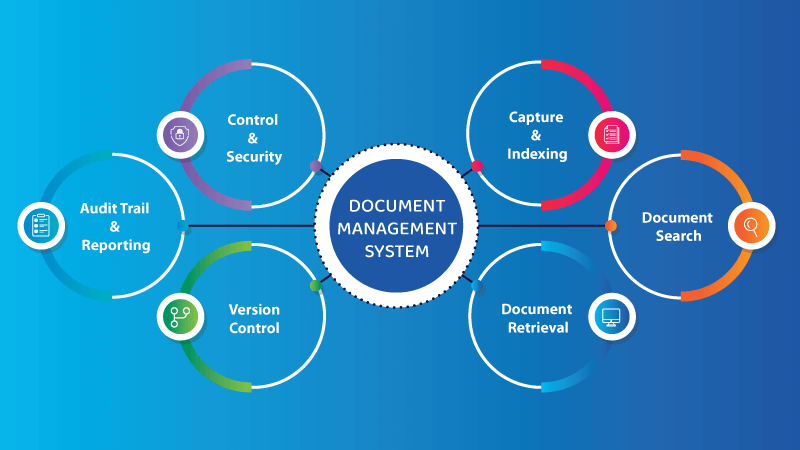
Document management is how businesses store, organize, retrieve, and control access to files.

Most businesses use a document management system (DMS) to centrally manage documents. These are cloud storage platforms, such as Google Drive and Proton Drive, that allow teams to upload files, organize them into folders, set access permissions, and store everything in one place.

A good DMS reduces version confusion and duplicate work, while giving teams clear visibility into where important files are stored.

File management focuses on basic organization—folder structure, naming conventions, and storage locations. Document management builds on this foundation by introducing governance features such as version control, permissions, and activity tracking. If file management is a filing cabinet, document management is that cabinet plus a lock and a logbook.

Many businesses implement document management systems to centralize files and restore order. However, structure alone does not guarantee that sensitive information remains protected. Not all DMSs offer end-to-end encryption (new window), which means files can still be read by the provider. This results in a loss of control over data and exposes businesses to security risks—a breach of the provider’s system becomes a data breach. Maintaining control means business data remains protected, and access is restricted to authorized individuals only, no matter what happens to the provider.

Why Businesses Need a Method for Managing Documents

Poor document management causes problems you may have encountered:

  • It Slows Down Your Productivity: The most tangible cost of poor document management is wasted time. And research (opens in a new window) supports this—96% of employees have trouble finding the latest version of a document, and 83% are forced to recreate files because they can’t find the original documents. That means hours are wasted searching for and recreating files—time that could otherwise be spent on work that moves your business forward.
  • Causes confusion in collaborative work: When no one knows which version of a document is the latest, work gets duplicated, decisions are delayed, and mistakes happen. In distributed teams, this uncertainty spreads quickly, leading to missed deadlines and subpar results.
  • Accidentally exposing sensitive data: Weak access controls leave you vulnerable to breaches and careless mistakes. In a study of financial services companies, more than 64% (new window) had sensitive files accessible to any employee. Just one misconfigured folder is enough to expose client data and end a business relationship.

Making compliance harder to prove: In sensitive industries such as healthcare (new window) and finance, clear evidence is required regarding how documents are stored, accessed, and retained. If you cannot demonstrate compliance, you will face regulatory fines and damage client relationships.

6 Best Practices for Document Management

Here are six best practices to help you build an organized, secure, and user-friendly document management system.

1. Store your files in one location

Centralization makes finding the right file much easier and eliminates the need to search across multiple inboxes, local drives, and cloud accounts. Set rules and permissions that keep documents in one place, rather than scattered across multiple systems with different restrictions.

2. Create a folder structure and naming conventions—and apply them consistently

Organize folders by function or department (marketing, finance, HR, etc.), then by consistent subcategories such as year, project, or client name. For file names, include identifiers that make them easy to find, such as the date, version number, and document type: ClientName_Contract_2025-01-15_v2.pdf. This is much easier to find than “Final_revised_FINAL.pdf.”

3. Control who has access to sensitive documents

Not every employee needs access to every document in a company—a graphic designer, for instance, has no need to view employee records or financial reports. Establish permissions that restrict document access to the appropriate individuals, and review these permissions periodically. Permissions that remain active after a role change, project completion, or an employee’s departure create hidden security and privacy liabilities. If your team handles financial records, customer information, or product plans, maintaining confidentiality is simply part of doing business. Losing track of who has access to such data can lead to regulatory scrutiny, the loss of business deals, and reputational damage.

4. Track versions carefully

Picture this: five employees are editing five different copies of the same document. Which one should you use? When work passes through many hands, version control becomes essential. Tools such as collaborative document platforms—which allow your team to work on the same file simultaneously—make version control much easier. Changes are visible as they happen. Features like inline comments, suggested edits, and version history reduce the back-and-forth exchanges that can slow a team down, especially when members are working across different time zones.

5. Protect externally shared files with passwords

Sensitive files often need to be shared with investors, partners, or customers. When sharing externally, follow a simple rule: access should remain identifiable, time-limited, and easily revocable. Use sharing links protected by passwords and expiration dates, rather than open links or email attachments. This ensures that access remains under your control—you can monitor who has access, limit the duration of that access, and revoke it whenever necessary.

6. Choose a DMS with a strong security foundation

Familiar tools like Google Drive offer a practical solution, but this convenience often comes at the expense of privacy and security. A fully encrypted DMS ensures that files are encrypted before they leave your device, with decryption possible only for the sender and the intended recipient.

Unsure which platform to choose? Ask who holds the encryption keys and under which jurisdiction the provider operates. This reduces the risk of sensitive business data being read, leaked, or misused. It also influences the strength of your security defenses in the event of an incident, audit, or legal dispute.

Unlocking Convenience: Smart Garage Doors ExplainedUnlocking Convenience: Smart Garage Doors Explained

| 0 Comment |

Smart Garage Doors: The Future of Home Access and Security

Smart Garage Doors are revolutionizing the way homeowners access their garages, offering enhanced convenience and security through advanced technology. As part of the growing trend of smart home devices, these doors can be controlled remotely via smartphones or smart home systems, providing a seamless integration of home automation and security.

Transform your garage experience with automated garage door openers with app integration, allowing you to control access from anywhere at your convenience.

Embracing Smart Garage Doors means more than just innovation; it’s about ensuring safety and efficiency for homeowners. These systems allow for real-time monitoring and control, giving users peace of mind knowing their property is protected while also enjoying the luxury of modern technology. In today’s fast-paced world, time efficiency is paramount, and smart garage doors are here to enhance that.

One of the key features of Smart Garage Doors is their ability to connect to the internet, enabling users to control them from anywhere. Whether you’re at work, on vacation, or just lounging at home, you can open or close your garage door with a tap on your phone. This level of convenience not only improves the user experience but also enhances the security of your property, reducing the risk of unauthorized access.

Moreover, Smart Garage Doors often come with additional features such as integrated cameras and sensors that provide real-time alerts of any activity around your garage. This proactive approach to security helps homeowners stay informed and take action if needed. As technology evolves, Smart Garage Doors are becoming an essential component of a modern and secure home.

In summary, Smart Garage Doors represent a significant step forward in residential security and accessibility, merging convenience, safety, and technology into one comprehensive system that caters to the needs of the modern homeowner.

Experience the ultimate convenience of home automation with wifi-enabled garage door controllers that streamline your daily routines.

Benefits of Smart Garage Doors

Increased security features of smart garage doors are one of their most compelling advantages. With remote monitoring capabilities, users can receive alerts directly to their devices if the garage door is opened or closed, and integrated cameras can provide a live view, keeping intruders at bay and ensuring peace of mind.

Enhancing your property’s security is easy with smart garage security and monitoring systems that keep watch even when you’re away.

Energy efficiency and cost savings is another benefit of Smart Garage Doors. Many models are designed with better insulation and the option to close automatically, thus preventing heated or cooled air from escaping. This not only leads to reduced energy bills but also contributes to a smaller carbon footprint.

The convenience of remote access and control cannot be overstated. Whether you’re arriving home with groceries, letting a visitor in, or checking whether you left the garage door open, smart technology simplifies these tasks. Many systems are compatible with voice assistants, further enhancing user experience.

Furthermore, investing in Smart Garage Doors can boost property value. Homebuyers increasingly favor properties equipped with modern technology, viewing it as a sign of a well-maintained and updated home. As the real estate market evolves, these features will continue to become more sought after.

Lastly, the ability to integrate with smart home systems amplifies the benefits of Smart Garage Doors. They can work alongside other devices, such as smart security cameras and lighting, creating a cohesive smart home experience that enhances both functionality and security.

Installation of Smart Garage Doors

For those considering a DIY approach, installing a Smart Garage Door can be straightforward with the right tools and preparation. It’s essential to carefully follow the manufacturer’s instructions and ensure that all components are compatible and correctly wired to prevent operational issues.

Alternatively, opting for professional installation services can alleviate the hassle, especially for those unfamiliar with technology or construction. Professionals can guarantee a correct setup, optimizing functionality, and often offer warranty services that provide peace of mind.

Exploring smart garage door opener technology reveals several innovations, including battery backups for power outages, smartphone access, and customization features that allow for personalized settings tailored to individual needs. These advancements greatly enhance user experience.

Common installation challenges exist, such as alignment issues or compatibility with existing garage structures. Fortunately, many manufacturers provide troubleshooting guidelines, and a little research can help homeowners tackle these challenges effectively.

Cost factors for installing Smart Garage Doors can vary widely based on brand, features, and installation methods. It’s essential to budget not only for the door and opener but also for any necessary hardware, labor, or additional smart home integration options that might be desired.

Maintenance of Smart Garage Doors

Routine checks for smart garage door systems are crucial to ensure their longevity and functionality. Users should regularly inspect hardware for wear, test safety features such as auto-reversing mechanisms, and update software as needed to maintain security.

Troubleshooting common issues with smart garage doors involves checking power sources, resetting the system when facing connectivity problems, and ensuring that sensors are clean and unobstructed to facilitate smooth operation.

Maintaining smart garage door sensors is particularly important; they require regular cleaning to remove any obstructions like dirt and spider webs that might prevent them from functioning accurately. Ensuring proper alignment also plays a critical role in their reliability.

Enhancing the longevity of smart garage doors includes taking care of mechanical components, lubricating moving parts, and ensuring that the door closes properly. Regular maintenance decreases the likelihood of costly repairs and downtime.

Cleaning and care tips for smart garage door components suggest using mild soapy water for surface cleaning and avoiding harsh chemicals that could damage finishes or electronics. Regular inspections should also be performed to detect any signs of rust or corrosion.

Technology Behind Smart Garage Doors

An overview of smart garage door technologies reveals that they incorporate a mix of smart sensors, mobile app connectivity, and remote control mechanisms to enhance functionality. Most models offer features that can be customized according to user preferences.

Connectivity options like Wi-Fi, Bluetooth, and Z-Wave play a significant role in smart garage door technology. These allow homeowners to access their garage doors from various distances and enable integration with other smart home devices, leading to enhanced user control.

Features of mobile apps for control include remote opening and closing, notifications when the door is used, and live camera feeds for monitoring activity. These features empower users to stay informed and maintain security from anywhere.

Safety features built into smart garage doors encompass automatic reversal systems if an obstacle is detected, secure encryption to protect data, and emergency release mechanisms to ensure manual operation during power outages.

As for future trends in smart garage door technology, advancements may drive more robust integration with artificial intelligence, further enhancing security through facial recognition, predictive analytics for maintenance needs, and even automated troubleshooting for common issues.

Smart Garage Door Brands

Top brands in the smart garage door market include Chamberlain, Genie, and LiftMaster, each offering a variety of models with unique features tailored to different needs and preferences, ensuring homeowners have options to choose from.

A comparative analysis of features and pricing across these brands helps consumers make informed decisions. Factors such as warranty coverage, smart features, and installation costs are essential when evaluating products.

User reviews and satisfaction ratings often highlight the reliability and effectiveness of smart garage doors, with many customers expressing appreciation for the convenience and security they provide, although some may report intermittent connectivity issues.

Customer support and warranty options offered by brands significantly influence buyer confidence. Ensuring reliable support can save homeowners from potential headaches regarding installation and troubleshooting after purchase.

Innovative products from leading brands continue to emerge, such as smart locks integrated with garage door openers and advanced sensors that enhance security. Keeping an eye on these developments can benefit consumers looking for the latest in technology.

Integration with Home Automation

Connecting smart garage doors to home networks enables seamless access and control through various devices, creating an interconnected smart home environment that enhances user experience and convenience.

The benefits of integration with smart home devices extend to improved security and efficiency. For example, pairing garage doors with security cameras can provide comprehensive monitoring and alerts for any unauthorized access.

The use of voice control for garage doors through popular platforms like Amazon Alexa or Google Assistant adds a layer of convenience, allowing users to operate their doors with simple voice commands, which is particularly helpful when hands are full.

Automated schedules for smart garage doors further enhance usability. Homeowners can set specific times for the garage door to open or close, providing an element of personalization that fits their daily routines.

Lastly, security alerts and notifications integration ensures that users stay informed about any activity concerning their garage doors, helping to mitigate potential security risks and fostering a proactive approach to home safety.

Benefits of Sectional Garage Doors for Australian HomesBenefits of Sectional Garage Doors for Australian Homes

| 0 Comment |

Key Takeaways

  • Enhanced home worth
  • Sound dampening advantages
  • Suitability for varying weather conditions
  • Security characteristics for residential properties

Increased Property Value

Investing in sectional garage doors can significantly enhance the overall value of a property. These modern doors not only improve aesthetics but also provide a sense of security and functionality that appeals to potential buyers. In an increasingly competitive real estate market in Australia, features such as insulation, variety in design, and technology integration can make a home stand out. In metropolitan areas where property prices are on the rise, an attractive garage door can serve as a pivotal selling point, increasing buyer interest and potentially leading to higher offers.

Enhanced kerb appeal associated with sectional doors is another crucial factor contributing to increased property value. Homeowners can choose from a range of materials, colors, and styles to match their property’s exterior, ensuring cohesion and sophistication. The durability of sectional doors enhances their attractiveness for buyers, reducing potential maintenance concerns. Buyers are often attracted to properties that require minimal immediate investment after purchase, making sectional garage doors a wise upgrade that yields tangible returns during sale processes.

Appeal to Potential Buyers in the Real Estate Market

Sectional garage doors enhance the overall aesthetic of a property, significantly increasing its appeal to potential buyers. The modern and streamlined design provides a contemporary touch that complements various architectural styles prevalent in Australian suburbs. Home buyers often seek features that add both functionality and style to a property, making sectional doors a desirable choice. Their smooth operation and tailored designs can be particularly attractive to those looking for a home that requires minimal maintenance while offering high visual impact.

An investment in sectional garage doors can also lead to a more favorable perception of the property’s value. Buyers typically appreciate the versatility these doors offer, as they can be customized in various materials and colors to match the homeowner’s preferences. This tailoring aspect not only enhances curb appeal but also signals that the property has been well-maintained. The security features associated with sectional garage doors, such as robust locking mechanisms, further bolster buyer confidence, positioning the home as a safe and sound investment in the competitive Australian real estate market.

Feature Benefits Customisation Options
Aesthetic Appeal Enhances overall visual impact of the property Multiple colors and finishes available
Functionality Smooth and reliable operation Various materials like steel, aluminium, and timber
Maintenance Low maintenance requirements Custom designs tailored to individual preferences
Security Improved safety with robust locking mechanisms Advanced security features available
Value Addition Increases perceived property value Compatible with different architectural styles

Noise Reduction Benefits

A notable advantage of sectional garage doors is their capacity for noise reduction, which enhances the living experience within a household. These doors often incorporate advanced spring systems and insulated panels that effectively dampen sound transmission. Homeowners in urban settings, where external noise can be a significant disturbance, appreciate this feature as it allows for a quieter atmosphere in both the garage and adjoining living spaces. The use of high-quality materials in the construction of sectional doors further supports this noise-minimizing capability, ensuring that the clattering sounds of vehicles or heavy equipment are considerably muted.

In addition to reducing unwanted noise from outside, sectional garage doors also operate with a level of quietness that is beneficial for the entire household. The smooth glide of these doors, often bolstered by modern technologies such as polymer rollers and sturdy guide tracks, creates minimal operational noise. Families, particularly those with young children or individuals with different schedules, find this silent functionality particularly advantageous. By investing in high-performance sectional garage doors, homeowners not only enjoy a stylish and functional entryway but also a serene environment free from the distractions of disruptive sounds.

Quiet Operation with Advanced Spring Systems

Modern sectional garage doors are engineered with advanced spring systems that significantly enhance their quiet operation. These systems utilize high-quality torsion springs that are designed to distribute weight evenly and minimize noise during opening and closing. Not only does this feature contribute to a peaceful home environment, but it also enhances the overall user experience, making it easier for homeowners to operate their garage doors at any time of day or night without disturbing the household.

The quiet functionality of sectional doors is particularly beneficial in densely populated areas where noise control is essential. By integrating noise-reducing features, these doors meet the needs of families seeking a tranquil living space while maintaining convenience. Additionally, these systems are designed for longevity and reliability, ensuring that the doors operate smoothly for years, providing homeowners with peace of mind alongside their functional benefits.

Climate Adaptability

Sectional garage doors are specifically designed to withstand varying climatic conditions, making them an ideal choice for Australian homes. Their construction typically features high-quality materials that provide thermal insulation, helping to regulate the internal temperature of the garage. This insulation not only contributes to energy efficiency but also protects vehicles and belongings from extreme heat or cold. The materials used, such as steel or insulated panels, are chosen for their durability and resistance to the Australian elements, including intense sun, torrential rain, and coastal salt air.

Furthermore, these doors are engineered to perform reliably in both high humidity and dry conditions. The seals and weather stripping play a critical role in preventing water ingress, ensuring that garages remain dry even during heavy downpours. This resilience extends to protection against wind pressure and debris, factors often encountered in storm-prone regions. Homeowners can enjoy peace of mind knowing that their sectional garage doors are built to endure Australia’s diverse weather challenges while enhancing the overall functionality of their property.

Resistance to Harsh Weather Conditions

Sectional garage doors offer remarkable durability against the extreme weather conditions often experienced across Australia. Designed with high-quality materials such as steel and insulated panels, these doors are built to withstand intense heat, heavy rain, and gusty winds. Many brands incorporate weather seals that prevent water intrusion and block out dust, ensuring that the garage remains a safe haven for vehicles and belongings alike. This level of resilience is particularly beneficial in coastal regions where salty air can corrode lesser materials.

Furthermore, sectional garage doors feature a robust structural integrity that helps prevent warping or bending, which can be common with traditional single-panel designs. Their multi-sectional design allows for a seamless fit against the frame, significantly reducing the chances of damage during storms. Homeowners can expect not only an enhancement in functionality but also a reliable barrier against harsh climatic elements. Investing in these doors reflects a proactive approach to safeguarding property while ensuring long-term performance.

Safety Features for Family Homes

Modern sectional garage doors are equipped with a variety of safety features designed to protect families in their homes. Automatic reversal systems play a vital role in enhancing safety by sensing obstacles when the door is closing. If an object or person comes in contact with the door’s pathway, the mechanism will reverse its motion immediately, preventing injuries and property damage. Additionally, advanced sensor technology enhances the reliability of these features, ensuring optimal functionality for Australian households.

Another critical aspect is the incorporation of pinch-resistant joints that prevent fingers from getting caught during operation. This feature is particularly beneficial in homes with young children or pets. Manufacturers have also prioritised the use of high-quality materials that can withstand external pressures while ensuring a secure closure. Incorporating these elements into the design significantly improves the overall safety profile of sectional garage doors, making them a wise choice for safety-conscious homeowners.

Automatic Reversal and Sensor Technology

Modern sectional garage doors incorporate advanced automatic reversal and sensor technologies that enhance safety for families. These features are crucial for preventing injuries by ensuring that the door reverses direction if an obstruction is detected. Whether it’s a child, a pet, or any object in the path of the door, these sensors are designed to provide immediate feedback that commands a halt in operation. This technology significantly reduces the risk of accidents, making these doors an excellent choice for households with children or pets.

In addition to safety, the implementation of sensor technology contributes to the overall convenience of garage operations. Many models are equipped with remote controls that allow users to open and close the door at a distance. Some systems can even integrate with smart home devices, enabling homeowners to monitor and manage their garage access via smartphone applications. This blend of technological advancements creates a more secure and user-friendly experience, appealing to modern Australian homeowners who value both functionality and peace of mind.

  • Automatic reversal systems prevent accidents by detecting obstructions in the door’s path.
  • Advanced sensors offer real-time feedback to halt garage door operation if necessary.
  • Remote controls provide the convenience of opening and closing the door from a distance.
  • Some models feature integration with smart home systems for added control and monitoring.
  • Enhanced security features protect homes from unauthorized access.
  • Regular maintenance of sensor technology ensures optimal performance and safety.
  • User-friendly designs cater to the needs of modern Australian families.

FAQS

What are the advantages of installing sectional garage doors in Australian homes?

Sectional garage doors offer several benefits, including increased property value, noise reduction, climate adaptability, and enhanced safety features. They are also designed to withstand harsh weather conditions commonly found in Australia.

How do sectional garage doors affect property value?

Sectional garage doors can significantly increase the appeal of a home to potential buyers, as they provide a modern look, improve functionality, and can enhance the overall aesthetic of the property, leading to a higher market value.

Are sectional garage doors noisy during operation?

No, sectional garage doors are designed with advanced spring systems that ensure quiet operation. This makes them an excellent choice for residential areas where noise reduction is a priority.

Can sectional garage doors withstand extreme weather conditions?

Yes, sectional garage doors are built to be resistant to harsh weather conditions, including heavy rain, wind, and temperature fluctuations, making them a durable option for Australian homes.

What safety features are included with sectional garage doors?

Sectional garage doors often come equipped with safety features such as automatic reversal and sensor technology, which help prevent accidents by detecting obstacles in the door’s path and reversing its direction if necessary.

A Child Oriented Approach to Toilet TrainingA Child Oriented Approach to Toilet Training

| 0 Comment |

A CHILD-ORIENTED APPROACH TO TOILET TRAINING
The online version of this article, along with updated information and services, is located on the World Wide Web at: pediatrics.org
Wrote: T. Berry Brazelton Pediatrics (1962)
Department of Pediatrics, Harvard Medical School, and the Massachusetts General Hospital and the Children’s Medical Center.

PEDIATRICIANS have a unique opportunity to prevent problems for the child in the area of bowel and bladder control. Since the advent of streamlined diaper care has liberated mothers in our culture from the real need to trainee their children early, this step may be viewed more honestly as a major developmental task for the child. Proper timing of this may enable him to achieve mastery for himself. The ultimate value of such self-achievement can be easily weighed against the adverse effects of inopportune training by an adult society.

The pediatric and psychiatric literature reports complications resulting from adverse toilet training. This paper will present the results of a program for training in which utilizing the child’s develop mental capacities and interest was the primary goal. Parents and pediatricians are aware that the child’s autonomous achievement in any developmental area frees him to progress to more advanced areas. Faulty mastery may leave him with a deficit that results in regression under stress. The relationship of coercive toilet training to chronic constipation has been pointed out.

Garrard and associates presented six cases of functional megacolon with psychogenic etiology, in which the environmental pres sure expressed in training practices were a primary factor. Glicklich5 summarized psychogenic factors in enuresis. Encopresis and urinary incontinenc can be traced to adverse or punitive training practices. Such pathologic symptoms usu ally reflect a fundamental psychologic disturbance in the child’s adjustment. But in healthful situations, parents can be encouraged to produce a positive reaction in the child to his control of bowel and bladder.

TOILET TRAINING

Local conditioning of reflex sphincter control can be effectively elicited as early as 9 months and has been the basis for an early introduction of@ Voluntary co-operation may be elicited as early as 12 to 15 months, and this period has been 79, 12, 15 as optimal for training. However, myelinization of pyramidal tracts to these areas is not completed until the twelfth to eighteenth month.

Associated with the transition from reflex compliance to a more voluntary type of developmental accomplishment, there is usually a perceptible time lag. In this period there is a kind of subtle inner resistance to outside pressure on the part of the child. This may be seen in many other developmental areas, such as reflex standing at 5 months to voluntary standing at 10 months, and vocalizations in the first year to verbal expressions in the latter half of the second year. This period is probably an important period of incorporation and of gathering inner forces for the child.

In a complex area such as toilet training, it would be even more likely that any training based on early reflex compliance would go through a subsequent periods of bag and breakdown before voluntary compliance on the part of the child could ensue. Postponed breakdown in a control achieved before 12 to 18 months is much more frequent than that seen when control is accomplished after 18 months.

That this breakdown in control can be circumvented by pressure from the environment is easy to see in some European cultures, where the incidence of postponed breakdown is much lower than in our own less rigid. However the severity and intractability of the symptoms produced in the deviant cases in these countries is good evidence for the strength of the child’s inner resistances, which bring about such breakdowns. The incidence of failure in England is reported as varying from 10 to 15%.

Grundfos Dosing All ProductGrundfos Dosing All Product

| 0 Comment |

With almost 18,000 employees worldwide, and annual production of 16 million pump units per year, Grundfos is one of the world’s leading pump manufacturers. The 80 Grundfos Companies around the globe help bring pumps to every corner of the world, supplying drinking water to Antarctic expeditions, irrigating Dutch tulips, monitoring groundwater beneath waste heaps in Germany, and air conditioning Egyptian hotels.

Efficient, sustainable products

Grundfos is constantly striving to make its products more user-friendly and reliable as well as energy-saving and efficient. Our pumps are equipped with ultra-modern electronics allowing output to be regulated according to current needs. This ensures convenience for the end-user, saves a great deal of energy and, in turn, benefits the environment.

Research and development

In order to maintain its market position, Grundfos takes customer research to heart when improving or developing new products. Our Research and Development department makes use of the latest technology within the pump industry in search of new and better solutions for the design and function of our pump solutions.

Corporate values

The Grundfos Group is based on values such as sustainability, openness, trustworthiness, responsibility, and also on partnership with clients, suppliers and the whole of society around us, with a focus on humanity that concerns our own employees as well as the many millions who benefit from water that is procured, utilized and removed as wastewater with the help of Grundfos pumps.

Grundfos Dosing All Product

Digital dosing pumps for high precision dosing of chemicals, enabling advanced control of process and integration with system control.

User Manual for the Corporate Sector Vulnerability UtilityUser Manual for the Corporate Sector Vulnerability Utility

| 0 Comment |

Amid an ever-increasing number of cyberattacks, safeguarding digital assets has become a major challenge for every organization. Every day, new security gaps—known as vulnerabilities—are discovered in software, systems, or networks that attackers can exploit. Therefore, vulnerability scanning and assessment are critical components of any cybersecurity strategy.

This activity is not just a task for the IT team, but a strategic investment in business continuity. With increasingly complex IT infrastructure—including the use of cloud and multi-cloud environments—the potential scope of attacks has expanded. This makes vulnerability management even more challenging, but also far more crucial.

This article will provide a comprehensive overview of vulnerability scanning and assessment, from the basics to practical implementation in the enterprise. You’ll gain an understanding of the methods, tools, best practices, and challenges involved in running an effective vulnerability management program.

Understanding the Differences: Vulnerabilities, Threats, and Risks

Before delving deeper, it’s important to understand the differences between vulnerabilities, threats, and risks in cybersecurity.

Vulnerability: This is a weakness or flaw in a system, application, or process that an attacker can exploit. Examples include bugs in program code, configuration errors, or system design flaws. These vulnerabilities are inherent in the system and can be identified through various testing methods.
Threat: This refers to an entity or event that has the potential to exploit a vulnerability to cause harm. Threats can include malware, hackers, insider threats, or even natural disasters. Threats are external in nature and possess both the motivation and the capability to launch an attack.
Risk: This is the likelihood of harm occurring if a vulnerability is exploited by a threat. Risk is calculated based on the combination of the likelihood of an attack occurring and the resulting impact. Understanding the relationship between these three concepts is essential for conducting an effective vulnerability assessment.

What Is Vulnerability Scanning?

Vulnerability scanning is an automated process for identifying, analyzing, and reporting security vulnerabilities in computer systems, networks, and applications. This process uses specialized tools that can detect known vulnerabilities by comparing the signatures, configurations, and behavior of the target system against a constantly updated vulnerability database.

Vulnerability scanning tools operate using various methods:

  • Network-based scanning: Analyzes systems from the perspective of an external attacker.
  • Host-based scanning: Analyzes the target system directly.
  • Application scanning: Focuses on identifying vulnerabilities in web applications and APIs.

Modern vulnerability scanners not only identify vulnerabilities but also provide additional information such as severity, exploit availability, patch information, and remediation guidance. This helps security teams prioritize remediation based on the actual risk to the organization.

Vulnerability Assessment: More Than Just a Scan

A vulnerability assessment is a more in-depth process than a simple scan. It involves a systematic evaluation of an organization’s security posture, including people, processes, and technology. This process not only identifies technical vulnerabilities but also analyzes the business context, threat landscape, and the organization’s risk tolerance.

An effective assessment combines automated scanning with manual testing. Security professionals will analyze the scan results in depth, validate the findings, and provide business-focused recommendations. This process also involves evaluating existing security controls and analyzing gaps against industry standards and best practices.

A comprehensive vulnerability assessment covers several areas: network infrastructure, operating systems, applications, databases, cloud services, mobile devices, and IoT devices. Each area has unique characteristics and challenges, requiring specialized approaches and tools.

Stages of Conducting a Vulnerability Assessment

Phase 1: Planning and Scoping

The first step involves thorough planning and the establishment of a clear scope. This includes identifying the assets to be assessed, setting a schedule, allocating resources, and coordinating with relevant parties. A well-defined scope is crucial to ensure adequate assessment coverage without disrupting business operations.

The scoping process must take into account business priorities, regulatory requirements, and the organization’s risk tolerance. Assets with high business importance should be given top priority. Communication with asset owners and business stakeholders is essential to understand dependencies and constraints that could impact assessment activities.

Comprehensive documentation regarding the scope, methodology, and success criteria must be prepared before the assessment begins. This ensures that all parties share a common understanding and provides a baseline for measuring the effectiveness of the assessment.

Phase 2: Asset Discovery and Inventory

Asset discovery is a foundational step in a vulnerability assessment. A comprehensive asset inventory is vital to ensure that no systems or applications are overlooked within the assessment scope. In modern corporate environments, “shadow IT”—unofficial systems not recorded in the formal inventory—is frequently present.

The asset discovery process employs a combination of automated tools and manual verification. Network discovery tools can identify active hosts, open ports, and running services. Cloud asset discovery tools are essential for environments that utilize public cloud services. Integration with Configuration Management Databases (CMDB) and asset management systems can enhance the accuracy and completeness of the inventory process.

Classifying assets based on their level of importance, data sensitivity, and business function helps in prioritizing assessment activities. Critical systems that handle sensitive data or support essential business functions should receive more intensive attention throughout the assessment process.

Phase 3: Scanning and Testing

The vulnerability scanning phase involves executing automated scans using various tools and techniques. Network vulnerability scanners—such as Nessus, OpenVAS, or Qualys—can identify vulnerabilities within network infrastructure and systems. Web application scanners, such as OWASP ZAP or Burp Suite, focus on application-level vulnerabilities.

Scanning strategies must strike a balance between comprehensive coverage and operational impact. Authenticated scans provide greater visibility into system configurations and installed software, but they require privileged access credentials. Unauthenticated scans simulate the perspective of an external attacker, though they may overlook internal vulnerabilities.

Scan scheduling must take business operations and network capacity into account. High-intensity scans can degrade system performance or cause service disruptions. Coordination with operational teams is essential to minimize business impact during scanning activities.

Phase 4: Analysis and Validation

Raw scan results require expert analysis to distinguish actual vulnerabilities from false positives. Security analysts manually verify high-severity findings to ensure accuracy and assess the likelihood of exploitation. Contextual analysis considers compensating controls, network segmentation, and access restrictions that may mitigate the impact of a vulnerability.

The validation process also involves correlating results from multiple scans and integrating them with threat intelligence feeds. Understanding active threats and exploitation trends helps in prioritizing vulnerabilities that are more likely to be exploited.

Assigning risk ratings requires considering technical severity, business impact, and the likelihood of exploitation. Standardized rating systems such as CVSS (Common Vulnerability Scoring System) provide a baseline, but organizational context must be taken into account when determining the final risk.

Implementing a Vulnerability Management Program

Establishing a Governance Framework

A successful vulnerability management program requires a clear governance structure with well-defined roles, responsibilities, and accountability. The governance framework should encompass policy definitions, procedural documentation, and performance metrics to measure the program’s effectiveness.

Executive support is crucial for securing necessary resources and ensuring organizational commitment to vulnerability management initiatives. A security steering committee can provide oversight and make strategic decisions regarding risk acceptance and resource allocation.

Integration with existing IT governance processes ensures that vulnerability management aligns with broader organizational objectives. Change management processes should incorporate vulnerability assessment results into the deployment approval workflow.

Establishing Operational Processes

Operational excellence in vulnerability management requires standardized processes for scanning, analysis, remediation, and reporting. Process documentation should include step-by-step procedures, escalation paths, and quality assurance checkpoints.

Automation plays a vital role in scaling vulnerability management operations. Automated scanning schedules, results processing, and notification systems can reduce manual effort and enhance consistency. Integration with IT Service Management (ITSM) systems enables a seamless workflow from vulnerability identification to the completion of remediation.

Metrics and KPIs are essential for monitoring process performance and identifying opportunities for improvement. Common metrics include the average time to remediate, patch compliance rates, and vulnerability trend analysis. Regular process reviews and optimization efforts ensure continuous improvement in the program’s effectiveness.

Integration with the Security Ecosystem

Modern vulnerability management does not operate in isolation; rather, it is integrated into the broader security architecture. Integration with a Security Information and Event Management (SIEM) system allows for the correlation of vulnerability data with security events, enhancing threat detection capabilities. Threat intelligence feeds provide context regarding vulnerabilities that are being actively exploited, enabling prioritization based on the actual threat landscape. Integration with endpoint detection and response (EDR) solutions can offer additional visibility into exploitation attempts.

Security orchestration platforms can automate response actions based on the results of vulnerability assessments. Automated patching for low-risk systems, adjustments to network segmentation, and the implementation of security controls can reduce the need for manual intervention.

Challenges and Best Practices

Managing False Positives

A high rate of false positives in vulnerability scanning can significantly impact program efficiency and analyst productivity. Fine-tuning scan configurations, regularly updating vulnerability signatures, and implementing baseline comparisons can help reduce false positive rates.

Training analysts in vulnerability validation techniques is essential for the accurate interpretation of results. Developing an organizational knowledge base regarding common false positives and validation procedures can improve consistency throughout the analysis process.

Providing feedback to tool vendors can help improve signature accuracy and lower false positive rates in future releases. Participating in vulnerability research communities also provides insights into emerging threats and detection techniques.

Prioritization and Risk-Based Approaches

Not all vulnerabilities pose the same level of risk to an organization. Risk-based vulnerability management focuses remediation efforts on those vulnerabilities with the greatest potential impact on business operations and data security.

Prioritization frameworks should account for technical severity, the criticality of business assets, the threat landscape, and compensating controls. Integrating business impact analysis and threat modeling provides the necessary context for risk-based decision-making.

Regularly reviewing and adjusting prioritization criteria ensures alignment with the evolving threat landscape and shifting business priorities. Feedback from incident response activities can inform improvements to risk assessment methodologies.

California’s Electricity Crisis: A Market Apart?California’s Electricity Crisis: A Market Apart?

| 0 Comment |

In the wake of California’s electricity market melt- down, a flood of analyses carried the ‘‘lessons’’ learned from the crisis to neighboring states and countries that had in turn been considering restructuring their electricity the California crisis.

Thus perhaps the most relevant lesson to take from California’s crisis is that electricity markets are neither naturally doomed to failure nor guaranteed easy success.

The factors most often cited as the causes of the California crisis are the scarcity of generation capacity (combined with rapid growth in demand), a ‘‘flawed’’ market design that included a freeze on retail rates, and the venality of electricity producers.

As the author describes in this paper, the market power of producers, California has earned a reputation as an incubator of instability, and system reliability problems that char-

The factors most often cited as the causes of the California and the venality of electricity producers. However, many of thes have suffered through anything like the California crisis. The contracts or other forms of long-term supply arrangements.

USA are the scarcity of generation capacity, a flawed market design, ributes were present in other electricity markets, none of which factor not seen in other markets in the world is the lack of forts are therefore best directed at developing a regulatory and reflective of underlying market conditions. other markets have experienced disruptions, no market press and venal producers.

Subsequent Events: The California Energy Crisis

California’s new wholesale electricity market and customer choice program, which began in March 1998, functioned fairly well for about a year and a half. In the summer of 2000, retail electricity prices in Southern California reached an all-time high, and a shortage of generation capacity forced temporary power outages in Northern California.

Since then, coverage of the California energy crisis has been reported on television and in newspapers across the country. The complexity of the issue, the contrasting viewpoints, and the sometimes conflicting solutions offered by politicians, government officials, and other stakeholders have made it difficult to keep track of what has happened.

To help provide a clearer picture of the situation, the following paragraphs present a broad perspective on this crisis.

Three Main Issues

California’s energy crisis can generally be grouped into three interrelated issues: (1) a drastic rise in wholesale electricity prices, (2) periodic power shortages during peak-demand periods, and (3) the deteriorating financial stability of California’s three major private utility companies—Pacific Gas and Electric (PG&E), Southern California Edison (SCE), and San Diego Gas and Electric (SDG&E).

High Wholesale Electricity Prices: Wholesale electricity prices traded on the newly formed California Power Exchange (CalPX) began to rise around June 2000, reaching unprecedented levels for the remainder of the year. From June 2000 to July 2000, wholesale electricity prices rose by an average of 270 percent compared to the same period in 1999.

In December 2000, wholesale prices on CalPX reached $376.99 per megawatt-hour (MWh), more than 11 times higher than the average price of $29.71 per MWh in December 1999.

High wholesale prices led to a sharp, though temporary, increase in retail electricity prices in Southern California during the summer of 2000. Here’s what happened. In July 1999, the SDG&E retail price freeze was lifted as mandated by California’s industry deregulation plan, and SDG&E customers were exposed to unregulated retail electricity prices (PG&E and SCE retail customers, at that time, were still protected from high retail prices by rate freezes imposed by the restructuring plan). SDG&E could now pass on high wholesale prices to retail customers, and by July 2000, residential electricity rates had risen to about 16 cents per kilowatt-hour, up from about 11 cents per kilowatt-hour in July 1999.

To curb rising retail prices, the California legislature set a cap of 6.5 cents per kilowatt-hour on the energy component of electricity bills for SDG&E’s residential, small business, and streetlight customers.

Scheduled Power Outages: Since 1999, California has experienced a significant increase in emergency conditions that, in some cases, have required rolling blackouts (rolling blackouts are forced reductions in electricity usage). Stage 3 emergency notices, which may require rolling blackouts, have increased from 1 in 2000 to 38 as of May 22, 2001 (see graph). Stage 1 and 2 alerts have increased from 91 in 2000 to 127 as of May 22, 2001. In some cases, Stage 2 requires voluntary reductions in electricity usage.

Factors Contributing to the Energy Crisis

Although there is no universal consensus regarding the causes of California’s problems, there is general agreement among industry leaders on a set of core factors that contributed to the energy crisis.

Investment in new power generation capacity has not kept pace with the growth in electricity demand. California’s power generation capacity declined by 2 percent between 1990 and 1999, while retail sales rose by 11 percent. Furthermore, no new power generation capacity had been built in California for over a decade.

To meet its energy needs, California relied on approximately 7 to 11 gigawatts of out-of-state generation capacity—much of it hydroelectric power located in the Pacific Northwest. A drop in hydroelectric production, caused by critically low water levels in the Pacific Northwest, resulted in reduced electricity imports into Northern California.

Throughout 2000, approximately 10 gigawatts of generation capacity were offline during periods of high demand, contributing to the electricity supply shortage.

Path 15, a high-voltage transmission line connecting Southern California to Northern California, frequently experienced congestion, limiting the flow of surplus power from the south to meet the deficit in the north.

Exacerbating the electricity shortage, many independent power producers were reluctant to sell electricity to PG&E and SCE due to the utilities’ financial troubles and uncertainty regarding payment for the power sold.

Flaws in the wholesale electricity market rules established under the state’s restructuring plan contributed to rising wholesale prices. Specifically, market rules required PG&E, SCE, and SDG&E to purchase all their electricity through CalPX. They were unable to enter into long-term energy contracts. When spot market wholesale prices spiked due to electricity shortages and rising generation costs, the utilities had no choice but to purchase power at those high prices. Rising natural gas prices and the high costs of meeting California’s power plant emission requirements also contributed to the increase in wholesale electricity prices.

The three utility companies paid high wholesale prices for their electricity but were unable to recover their costs because retail electricity prices were frozen. As previously mentioned, this situation resulted in the three utilities accumulating massive debt.

Actions Taken to Address the Energy Crisis

The following are measures taken by the California government and the federal government to help alleviate the energy crisis and implement permanent solutions to the problems California had been experiencing since the summer of 2000:

June 28, 2000: The California Public Utilities Commission (CPUC) lowered the purchase price cap to $500 per megawatt for real-time ancillary services and congestion management markets. The CPUC subsequently lowered this price cap again to $250 per megawatt on August 1, 2000.

August 3, 2000: The CPUC issued a rate stabilization plan for SDG&E. This plan was designed to provide electricity price relief for certain residential and commercial customers served by SDG&E.

August 30, 2000: The California legislature passed legislation (AB265) establishing a rate cap of 6.5 cents per kilowatt-hour for SDG&E customers. This rate cap was retroactive to June 2000 and was set to remain in effect until 2002.

December 14, 2000: The Secretary of Energy issued an order requiring certain power generators and electricity marketers to supply electricity to California’s power system operator to help prevent blackouts.

December 15, 2000: The Federal Energy Regulatory Commission (FERC) ordered corrective measures for California’s wholesale electricity market. The order, among other things, eliminated the mandatory requirement that the three investor-owned utilities (IOUs) sell and purchase all their electricity through CalPX. FERC also terminated the CalPX wholesale rate schedule that allowed it to continue operating. CalPX ceased operations in January 2001.

January 4, 2001: The CPUC granted PG&E and SCE a temporary surcharge to raise rates. This temporary surcharge was effective for 90 days. February 1, 2001: Governor Gray Davis signed legislation (AB 1X) authorizing the California Department of Water Resources to purchase electricity under long-term contracts for resale to PG&E and SCE. The legislation was passed partly because both utility companies were facing financial difficulties and were unable to secure long-term electricity contracts with power generators. This law was significant because the State became an active participant in California’s electricity industry.

March 27, 2001: The CPUC approved an average rate increase of 3 cents per kilowatt-hour in an effort to support PG&E and SCE, which were experiencing financial distress.

April 5, 2001: Governor Gray Davis released a plan to resolve the state’s energy crisis and protect residents from the volatile energy market. The plan included various elements aimed at increasing electricity supplies, boosting energy conservation, and stabilizing California’s electricity industry.

April 9, 2001: Governor Gray Davis announced an agreement with SCE and Edison International, SCE’s parent company. Under the agreement, SCE would sell its transmission system to the State of California for $2.76 billion. This sale was designed to help SCE recover from its financial difficulties. The agreement required approval by the State Legislature to be finalized.

April 25, 2001: FERC announced a plan to bring greater stability, improved control, and price relief to California’s energy market. Among other measures, the plan granted the California Independent System Operator (California ISO, which operates the state’s transmission system) greater control over power plant outages, established market-based price mitigation measures, and mandated new reporting requirements to enable FERC to better monitor California’s energy market. May 14, 2001: FERC announced regulatory actions to boost reliable energy supplies in California and other Western states. FERC streamlined regulatory procedures for wholesale electricity sales and the certification of natural gas projects. It also urged all hydroelectric power plant licensees to assess the potential for increasing generation capacity at their respective facilities.

May 15, 2001: In March, the California Public Utilities Commission (CPUC) approved retail electricity rate hikes for PG&E and SCE customers. Today, the CPUC released a rate structure specifying exactly which customer classes would face rate increases and the magnitude of those increases. Overall, retail rates will rise by an average of 19 percent; however, low-income customers, customers with medical baseline allowances, and residential customers consuming less than 130 percent of the standard usage baseline will be exempt from the rate increases.

Aggiornamento spazi confinati e lavori in quota confinati e spazi confinatiAggiornamento spazi confinati e lavori in quota confinati e spazi confinati

| 0 Comment |

Quando la formazione spazi confinati precedente all’ASR può essere ancora riconosciuta valida?

Sul tema dell’aggiornamento spazi confinati c’è una domanda che, dopo il nuovo Accordo Stato-Regioni 2025 sulla formazione in materia di salute e sicurezza, molti committenti, CSE, RSPP e HSE Manager stanno iniziando a porsi con una certa urgenza.

Un’impresa deve svolgere lavori in un ambiente sospetto di inquinamento o confinato. Presenta una dichiarazione nella quale afferma di essere in regola con la formazione spazi confinati, ma non ha ancora svolto il percorso secondo il nuovo Accordo Stato-Regioni oppure non ha ancora eseguito l’eventuale aggiornamento quinquennale secondo il nuovo schema formativo.

La domanda, quindi, è semplice solo in apparenza: quella formazione precedente può essere considerata ancora valida?

La risposta corretta è questa: la sola dichiarazione dell’impresa non basta.

La formazione pregressa può essere riconosciuta solo se l’impresa è in grado di dimostrare, con documenti oggettivi, che il corso già svolto aveva contenuti conformi a quelli oggi previsti dal nuovo Accordo per i lavori in ambienti sospetti di inquinamento o confinati. E, anche quando la formazione pregressa è riconoscibile, resta un secondo controllo decisivo: l’aggiornamento quinquennale è ancora nei termini oppure è già stato svolto?

Il punto, quindi, non è sapere se “prima avevano già fatto un corso”. Il punto è capire che cosa avevano fatto davvero, con quali contenuti, con quale verifica finale e con quale scadenza di aggiornamento.

Ed è proprio qui che la verifica documentale diventa decisiva.

Il periodo transitorio è scaduto: cosa cambia davvero

Il nuovo Accordo Stato-Regioni 2025 è stato pubblicato in Gazzetta Ufficiale n. 119 del 24 maggio 2025. Il testo prevede che, in fase di prima applicazione e comunque non oltre dodici mesi dall’entrata in vigore, potessero essere avviati corsi secondo gli Accordi Stato-Regioni abrogati e secondo il vecchio Allegato XIV del D.Lgs. 81/2008.

Seguendo il testo pubblicato in Gazzetta Ufficiale, il termine operativo dei dodici mesi è il 24 maggio 2026. Le FAQ del Ministero del Lavoro indicano invece come data di entrata in vigore il 19 maggio 2025, cioè la pubblicazione sul sito ministeriale. Per prudenza tecnica, possiamo quindi dire che il periodo transitorio si è concluso tra il 19 e il 24 maggio 2026, a seconda della fonte considerata.

Al di là di questa differenza di pochi giorni, il punto sostanziale non cambia: oggi il periodo transitorio è terminato.

Questo significa che non siamo più nella fase in cui era possibile avviare nuovi corsi secondo i vecchi Accordi Stato-Regioni. I nuovi percorsi formativi devono essere progettati ed erogati secondo il nuovo Accordo.

Attenzione però a non cadere nell’errore opposto: la fine del periodo transitorio non cancella automaticamente tutta la formazione svolta prima dell’Accordo. Non significa che ogni attestato precedente perda valore da un giorno all’altro. Significa invece che la formazione pregressa può essere riconosciuta solo nei casi e alle condizioni previste dal nuovo Accordo.

Per gli ambienti sospetti di inquinamento o confinati, la condizione è chiara: i corsi già erogati alla data di entrata in vigore dell’Accordo sono riconosciuti se i contenuti sono conformi al nuovo percorso previsto.

Dopo la scadenza del periodo transitorio, quindi, la domanda non è più: “L’impresa aveva già fatto un corso?”. La domanda diventa: “Quel corso precedente è davvero riconoscibile secondo il nuovo Accordo? I contenuti erano conformi? L’aggiornamento quinquennale è ancora valido? La documentazione riguarda i lavoratori che entreranno davvero nello spazio confinato?”.

Questo è il vero nodo operativo.

Il corso di aggiornamento combinato su spazi confinati e lavori in quota è un corso di sicurezza ad alto rischio della durata di 1 o 2 giorni che aggiorna le conoscenze dei lavoratori certificati in materia di identificazione dei pericoli, conformità legale e operazioni di soccorso in caso di emergenza.

Corso di aggiornamento sugli spazi confinati

Ispezione dei pericoli: Revisione dei test atmosferici, dei gas tossici e dell’ossigeno.

Permessi e ruoli: Aggiornamento delle conoscenze sui permessi di accesso, sul personale di riserva e sugli operatori che accedono.

Utilizzo delle attrezzature: Esercitazioni pratiche sull’uso di treppiedi, paranchi e autorespiratori.

Corso di aggiornamento sui lavori in quota
Prevenzione delle cadute: Rivalutazione dell’installazione delle imbracature di sicurezza, dei punti di ancoraggio e delle imbracature stesse.

Ispezione dei sistemi: Ispezione di scale, ponteggi e sistemi anticaduta.

Calcoli: Revisione delle distanze di sicurezza in caso di caduta e dei limiti di peso.

Formato e requisiti del corso
Prerequisiti: È necessario possedere una certificazione/attestato di completamento valido (in genere corsi come RIIWHS202E e RIIWHS204E).

Durata: In genere dalle 6 alle 8 ore per una sessione condensata e combinata, oppure suddivisa in diversi workshop pratici.

Valutazione: Include un ripasso della teoria e una valutazione pratica delle competenze fisiche.

Se preferisci, fammi sapere:
Il tuo settore o ruolo lavorativo (edilizia, petrolio e gas, industria manifatturiera, ecc.)
Se preferisci una sessione pratica in presenza o un ripasso teorico online.

Posso aiutarti a delineare eventuali unità legali specifiche o la documentazione che devi preparare.

Monitorizarea Torch in SarcinaMonitorizarea Torch in Sarcina

| 0 Comment |

Sarcina este o perioadă plină de speranță și provocări, una dintre acestea fiind gestionarea riscului de infecții care ar putea afecta atât mama, cât și copilul nenăscut. Profilul Torch reprezintă un instrument esențial în acest demers, oferind medicilor informații vitale pentru a asigura o sarcină sănătoasă.

Profilul Torch reprezintă un set complex de analize care detectează prezența unor infecții ce pot afecta sarcina și dezvoltarea fetală. Acest screening include teste pentru toxoplasmoză, rubeolă, citomegalovirus, herpes simplex și alte infecții specifice. Testarea se efectuează prin recoltarea unei probe de sânge și identificarea anticorpilor specifici fiecărei infecții.

Ce este Profilul TORCH?

Profilul TORCH nu desemnează un sindrom, ci un set de analize destinate detectării prezenței unor infecții specifice care pot afecta sarcina și dezvoltarea fetală. Acronimul TORCH cuprinde Toxoplasmoza (T), Alte infecții (O) cum ar fi sifilisul, hepatita B și virusul varicelo-zosterian, Rubeola (R), Citomegalovirusul (C) și Herpes simplex virus (HSV).

Rolul Profilului TORCH în Sarcină

Profilul TORCH este vital în identificarea anticorpilor specifici fiecărei infecții, permițând astfel evaluarea riscului la care este expus fătul. Prin detectarea timpurie a acestor infecții, este posibilă implementarea măsurilor de precauție și tratament necesare pentru a minimiza impactul asupra dezvoltării fetusului.

Testarea Profilului TORCH

Recomandată în perioada preconcepției și în timpul sarcinii, testarea TORCH include analiza pentru anticorpii IgG și IgM, care indică stadiul infecției și imunitatea mamei. Această distincție este crucială pentru stabilirea planului de îngrijire adecvat și pentru prevenirea transmiterii infecțiilor la făt.

Importanța diagnosticului precoce

Identificarea precoce a infecțiilor prin profilul TORCH permite intervenția medicală în timp util, reducând riscul de complicații cum ar fi avorturile spontane, moartea fetală in utero sau malformațiile congenitale. Este esențială testarea gravidelor cu simptome suspecte sau expuse riscului de infecție.

Managementul și prevenția

Pe baza rezultatelor testelor TORCH, medicii pot recomanda tratamente specifice pentru a controla infecția și a proteja fătul. De asemenea, se pot oferi sfaturi preventive, inclusiv evitarea expunerii la sursele de infecție și adoptarea unui stil de viață sănătos.

  • Toxoplasma gondii

Toxoplasma gondii este un protozoar din clasa Sporozoare, capabil să infecteze aproape orice mamifer, inclusiv oamenii. Acest parazit are un ciclu de viață complex, care implică transformarea prin trei forme principale – trofozoit, chist și oochist – fiecare având un rol distinct în transmiterea și persistența infecției. Pisicile, fiind gazdele definitive, joacă un rol crucial în ciclul de viață al parazitului, eliberând oochiștii în mediul înconjurător prin materiile fecale.

Toxoplasma gondii, un parazit intracelular obligatoriu, invadează și se reproduce în celulele gazdei. Predilecția pentru celulele sistemului nervos central, celulele retiniene și celulele sistemului reticuloendotelial subliniază potențialele complicații grave ale infecției, inclusiv leziuni cerebrale și afectări oculare. Parazitul poate determina formarea de chisturi în țesuturile gazdei, un mecanism de evadare a răspunsului imun, contribuind astfel la persistența pe termen lung a infecției și posibilitatea reactivării în cazul imunosupresiei.

Transmiterea Toxoplasma gondii

Toxoplasma gondii poate fi transmisă omului prin mai multe căi:

  • Ingestia de carne cruda sau insuficient preparată termic ce conține chisturi toxoplasmice.
  • Ingestia de alimente sau apă contaminate cu oochiști proveniți din fecalele pisicilor infectate.
  • Transmiterea verticală (transplacentară) de la mamă la făt, în cazul în care mama contractează infecția în timpul sarcinii sau imediat înainte de concepție.
  • Transfuzii de sânge sau transplant de organe de la donatori infectați.
  • Contactul direct cu materiile fecale ale pisicilor infectate, fie prin curățarea litierei, fie prin manipularea solului contaminat.

Ciclul de viață al Toxoplasma gondii

Ciclul de viață al Toxoplasma gondii implică două faze: una sexuată, care are loc doar în intestinul pisicilor (gazda definitivă), și una asexuată, care poate avea loc în orice mamifer, inclusiv oamenii (gazde intermediare).

  • În Pisici (Gazda Definitivă): Parazitul se reproduce sexuat, producând oochiști care sunt eliminați în materiile fecale. Oochiștii devin infecțioși după 1-5 zile în mediu, putând supraviețui și rămâne infecțioși pentru luni de zile sau chiar ani în condiții favorabile.
  • În Gazdele Intermediare (Inclusiv Oamenii): Ingestia de oochiști sau chisturi conduce la eliberarea trofozoitelor în intestin, care apoi invadează celulele gazdei și se reproduc asexuat. Trofozoitii pot forma chisturi în diverse țesuturi, inclusiv creierul, mușchii și retina, contribuind la persistența infecției și potențial la transmiterea ulterioară prin consumul de carne contaminată.

Implicații fiziopatologice

După infectarea inițială, majoritatea persoanelor dezvoltă o formă latentă de infecție, cu formarea de chisturi care pot rămâne în țesuturi pentru tot restul vieții. În cazul imunosupresiei, aceste chisturi pot reactiva, ducând la manifestări clinice severe, cum ar fi toxoplasmoza cerebrală în cazul persoanelor cu HIV/SIDA. La femeile gravide, infecția primară poate traversa placenta, afectând dezvoltarea fetală și conducând la complicații grave, inclusiv avort spontan, nașterea prematură și malformații congenitale.

Prevenția infecției cu Toxoplasma gondii implică măsuri de igienă alimentară, evitarea expunerii la fecalele de pisică și, în cazul femeilor însărcinate, testarea serologică pentru a identifica expunerea recentă sau existența imunității preexistente. Monitorizarea serologică și, dacă este necesar, tratamentul în timpul sarcinii pot reduce semnificativ riscul de transmitere a infecției la făt.

Transmisia verticală (De la mamă la făt)

Transmisia Toxoplasma gondii de la mamă la făt se poate întâmpla dacă mama contractează infecția în timpul sarcinii, mai ales în timpul primului trimestru. Parazitul traversează bariera placentară, infectând fătul. Riscul de transmitere crește cu avansarea sarcinii, dar consecințele sunt de obicei mai severe dacă infecția are loc mai devreme în timpul sarcinii.

Efecte asupra fătului

  • Toxoplasmoza congenitală: Este forma cea mai severă a bolii și poate include o gamă largă de simptome, de la ușoare la grave. Efectele includ leziuni cerebrale, calcificări intracraniene, hidrocefalie (acumularea excesivă de lichid în creier) sau microcefalie (dimensiunea anormal de mică a capului).
  • Defecte oculare: Inflamația retinei (corioretinită) este comună și poate duce la scăderea vederii sau la orbire. Afectarea oculară poate să nu fie evidentă la naștere, manifestându-se mai târziu în viață.
  • Retard de creștere intrauterin: Infecția poate încetini creșterea fătului în uter.
  • Anomalii ale Sistemului Nervos: Inclusiv convulsii, retard psihomotor și dificultăți de învățare.
  • Alte efecte: Pot include surditate, icter, hepatosplenomegalie (mărirea ficatului și a splinei), anemie și trombocitopenie (scăderea numărului de plachete sanguine).

Rolul Anticorpilor IgG și IgM în diagnostic și monitorizare

  • Anticorpii IgM sunt produse rapid după infecție, indicând o expunere recentă la Toxoplasma gondii. Acești anticorpi ating un nivel maxim în aproximativ o lună și pot persista în concentrații scăzute până la doi ani. Prezența IgM-urilor este crucială pentru diagnosticarea infecțiilor recente, oferind o fereastră timpurie în detectarea și intervenția medicală adecvată.
  • Anticorpii IgG apar după IgM și persistă pentru o perioadă îndelungată, adesea pe tot parcursul vieții persoanei. Prezența IgG-urilor indică o expunere anterioară la parazit și, în general, conferă o imunitate protectoare. În contextul sarcinii, determinarea nivelurilor de IgG este vitală pentru evaluarea riscului de transmitere a infecției la făt. Femeile cu IgG pozitive înainte de sarcină au un risc scăzut de transmitere a infecției, în timp ce seroconversia și apariția IgG în timpul sarcinii indică o infecție recentă cu un risc semnificativ de transmitere verticală.

Implicații și Recomandări

  • Evaluarea Preconcepțională: Testarea serologică pentru anticorpii IgG și IgM împotriva Toxoplasma gondii este recomandată femeilor care plănuiesc să devină însărcinate pentru a evalua riscul de transmitere a infecției la făt.
  • Prevenția în timpul Sarcinii: Femeile însărcinate ar trebui să adopte măsuri de precauție pentru a reduce riscul de expunere la Toxoplasma, inclusiv evitarea consumului de carne crudă sau insuficient preparată și a contactului cu fecalele de pisică.
  • Monitorizarea Serologică: Femeile seronegative la începutul sarcinii ar trebui monitorizate periodic pentru detectarea oricărei seroconversii, ceea ce ar indica o infecție recentă și necesitatea intervenției medicale pentru protecția fătului.

Concluzie

Toxoplasma gondii reprezintă o provocare semnificativă în sănătatea publică, mai ales în contextul sarcinii. Înțelegerea modului de transmitere, a ciclului de viață al parazitului și a implicațiilor anticorpilor IgG și IgM în diagnosticul și monitorizarea infecției este esențială pentru prevenirea complicațiilor asociate toxoplasmozei. Prin abordări proactive de prevenție și monitorizare, se pot reduce semnificativ riscurile pentru sănătatea maternă și fetală.

  • Virusul rubeolei

Este cauza unei infecții exantematoase tipice copilăriei, aparține familiei Togaviridae și este un togavirus cu ARN monocatenar. Este notabil pentru specificitatea sa strict umană, cu transmitere aerogenă prin secreții nazofaringiene, având o perioadă de incubație de aproximativ 2-3 săptămâni. Deși adesea infecția este subclinică sau prezintă simptome ușoare, cum ar fi febră și erupții maculo-papulare, rubeola poate avea consecințe devastatoare dacă este contractată de femei gravide, în special în primele patru luni de sarcină, ducând la sindromul rubeolic congenital. Acest sindrom poate include o gamă largă de defecte congenitale severe, de la cataractă și surditate, până la hepatosplenomegalie și diverse malformații cardiace.

Imunitatea la rubeolă, obținută fie natural, prin infecție, fie prin vaccinare, este considerată pe viață și se manifestă prin prezența anticorpilor specifici IgG. Testarea pentru anticorpii IgM și IgG este crucială în diagnosticarea și monitorizarea răspunsului imun, IgM indicând o infecție recentă, în timp ce IgG sugerează o expunere anterioară sau o imunitate dobândită. Răspunsul imun eficient și persistent reprezintă o barieră importantă împotriva transmiterii intrauterine a virusului, protejând astfel fătul în cazul reinfecției sau expunerii secundare a mamei.

Introducerea vaccinului antirubeolic a redus semnificativ incidența infecțiilor congenitale, deși izbucnirile sporadice continuă să apară, subliniind importanța screening-ului pentru statusul imun înainte de sarcină și necesitatea vaccinării în rândul populațiilor susceptibile. Vaccinarea femeilor gravide este contraindicată datorită riscului teoretic de teratogenitate, accentuând necesitatea evaluării imunității preconcepționale și a planificării vaccinării.

Fiziopatologia și Impactul asupra fătului

Virusul rubeolei invadează organismul gazdă prin căile respiratorii superioare, replicându-se local înainte de a se disemina limfatic și hematogen în tot corpul. Impactul asupra fătului este profund, în special dacă infecția maternă se întâmplă în primul trimestru de sarcină, perioadă în care toate organele fătului se dezvoltă activ. Virusul poate traversa bariera placentară și infecta fătul, cauzând sindromul rubeolic congenital (SRC), caracterizat prin anomalii multiple, inclusiv surditate, cataractă, defecte cardiace congenitale, retard de creștere intrauterin și hepatosplenomegalie. SRC este rezultatul direct al efectelor citopatice ale virusului asupra celulelor fetale și a răspunsului imun al fătului la infecție.

Virusul rubeolei are capacitatea de a trece bariera placentară, infectând astfel fătul. Odată ce virusul ajunge la făt, acesta poate afecta diverse organe și sisteme în dezvoltare, determinând o gamă largă de anomalii congenitale. Mecanismele exacte prin care virusul rubeolei cauzează aceste defecte nu sunt pe deplin înțelese, dar se crede că virusul interferează cu diviziunea celulară și poate induce moartea celulară în țesuturile în curs de dezvoltare.

Principalele consecințe ale SRC

  • Defecte cardiace: Cele mai frecvente sunt defectele septale, stenoza arterei pulmonare și persistența canalului arterial.
  • Deficiențe senzoriale: Surditatea este una dintre cele mai comune manifestări ale SRC, datorită afectării cohleare. Cataracta și alte defecte oculare pot apărea, de asemenea, afectând grav vederea.
  • Retardul de creștere intrauterin: Bebelușii pot avea o greutate mică la naștere și pot prezenta semne de retard de creștere.
  • Hepatosplenomegalie: Mărirea ficatului și a splinei poate fi un semn timpuriu al SRC.
  • Anomalii neurologice: Inclusiv retard psihomotor și microcefalie.

Modalitate de transmitere

Transmiterea virusului rubeolei se realizează aerogen, virusul fiind prezent în secrețiile nazofaringiene ale persoanelor infectate. Este extrem de contagios, cu o capacitate ridicată de a se răspândi în colectivități, în special în lunile de iarnă și primăvară. Perioada de incubație variază între 14 și 21 de zile, iar persoanele infectate devin contagioase cu aproximativ o săptămână înainte de apariția erupției și rămân astfel până la aproximativ 7-14 zile după.

Prevenția infecției cu Virusul Rubeolei

Prevenția rubeolei se bazează în principal pe vaccinarea eficientă a populației. Vaccinul MMR (rujeolă, oreion, rubeolă) este sigur și eficient, conferind imunitate pe termen lung împotriva acestor boli. Vaccinarea femeilor în vârstă fertilă este deosebit de importantă pentru prevenirea SRC, deoarece vaccinul este contraindicat în timpul sarcinii. Femeile care planifică o sarcină ar trebui testate pentru imunitatea la rubeolă și vaccinate dacă sunt susceptibile, cu condiția să evite sarcina pentru cel puțin o lună după vaccinare.

Screening-ul pentru anticorpii specifici IgG împotriva rubeolei face parte din îngrijirea prenatală standard în multe țări, permițând identificarea femeilor gravide susceptibile la infecție. Strategiile de prevenție includ de asemenea practici bune de igienă respiratorie și evitarea contactului cu persoane infectate.

Concluzii

Rubeola rămâne o preocupare majoră de sănătate publică, în special din cauza potențialului său teratogenic. Eforturile de prevenție, în special vaccinarea și screening-ul prenatal, sunt esențiale pentru controlul rubeolei și prevenirea SRC. Având în vedere gravitatea consecințelor infecției rubeolice în timpul sarcinii, îngrijirea prenatală trebuie să includă evaluări riguroase ale imunității la rubeolă și să ofere consiliere adecvată privind vaccinarea pentru femeile la vârstă reproductivă.

  • Virusul citomegalic (CMV)

este un agent patogen persistent și ubiquitar din familia Herpesviridae, care include, de asemenea, virusul herpes simplex și virusul varicelo-zosterian. CMV poate cauza o gamă largă de manifestări clinice, de la infecții asimptomatice la boli severe la nou-născuți și persoane imunocompromise. Înțelegerea completă a CMV implică explorarea modurilor de transmitere, efectelor asupra diferitelor populații, mecanismelor de persistență și latență, precum și opțiunile de prevenție și tratament.

Transmiterea CMV

CMV se transmite prin contact direct cu fluidele corporale infectate, cum ar fi saliva, urina, lacrimile, sperma, secreția vaginală, și laptele matern. Infecția poate fi transmisă de la mamă la făt în utero (transmisie verticală), la naștere prin contact cu secrețiile cervicale și vaginale, sau postnatal prin alăptare. Transmisia nosocomială poate avea loc prin transfuzii de sânge și transplanturi de organe, având în vedere prezența virusului în leucocite.

Deși adesea asimptomatică, infecția primară cu CMV la adulți poate să se manifeste prin simptome similare mononucleozei infecțioase, inclusiv febră, oboseală, adenopatii, și uneori hepatită cu icter. Diferența majoră este absența anticorpilor heterofili, prezenți în mononucleoza cauzată de virusul Epstein-Barr.

Gravidele reprezintă o categorie deosebit de vulnerabilă la infecția CMV, cu un risc semnificativ mai mare de complicații. Infecția primară în timpul sarcinii prezintă un risc înalt de transmitere verticală a virusului de la mamă la făt, cu potențiale efecte devastatoare, inclusiv surditate, microcefalie și hepatită fetală. Rata de transmitere și severitatea efectelor asupra fătului sunt maximizate dacă infecția are loc în primele patru luni de sarcină. Reactivările infecțiilor latente prezintă un risc mult mai scăzut de transmitere fetală.

CMV este cea mai frecventă cauză de infecție virală congenitală și poate duce la sindromul congenital CMV. Infecția congenitală cu CMV poate cauza o gamă largă de probleme de sănătate, inclusiv:

  • Surditate sensorineurală
  • Microcefalie (dimensiune anormal de mică a capului)
  • Retard de dezvoltare
  • Deficiențe vizuale sau cecitate
  • Hepatosplenomegalie (mărire anormală a ficatului și splinei)
  • Petele purpurii pe piele cunoscute sub numele de peteșii

Diagnosticul CMV se bazează pe detectarea virală directă prin cultură virală, PCR (reacția în lanț a polimerazei) pentru identificarea ADN-ului viral, sau prin testare serologică pentru a identifica prezența anticorpilor specifici IgM (indicând o infecție recentă) și IgG (indicând o infecție trecută sau o infecție cronică activă).

Răspunsul imun la CMV implică inițial producția de anticorpi IgM, urmată de dezvoltarea anticorpilor IgG. În timp ce IgM-urile ating un maxim și apoi scad în câteva luni, anticorpii IgG persistă și oferă un marker de infecție anterioară sau cronică activă. Reactivările sau reinfectările pot induce creșteri moderate ale titrurilor de IgG, dificil de distins în contextul imunodepresiei.

Prevenție și tratament

  • Prevenție: Include practici bune de igienă pentru a reduce răspândirea CMV, screening-ul donatorilor de sânge și de organe și evaluarea serologică a femeilor însărcinate pentru a identifica riscul de transmitere verticală.
  • Tratament: În cazurile severe sau la persoanele imunocompromise, antivirale precum ganciclovir, valganciclovir, foscarnet și cidofovir pot fi eficace în controlul infecției. Managementul include de asemenea monitorizarea și tratamentul complicațiilor asociate.

Vaccinare

Deși nu există încă un vaccin aprobat pentru prevenirea CMV, cercetările sunt în desfășurare pentru dezvoltarea unuia. Vaccinarea ar putea oferi o strategie importantă de prevenție, în special pentru femeile în vârstă fertilă, pentru a reduce riscul de transmitere congenital.

  • Virusul herpes simplex (HSV)

include două tipuri principale: HSV-1 și HSV-2, ambele fiind cauze comune ale infecțiilor virale la om. Diferențierea între aceste două tipuri este crucială din perspectiva managementului clinicii, a consilierii pacientului și a prevenirii transmiterii, în special în contexte sensibile cum ar fi sarcina și imunodepresia.

HSV-1

HSV-1 este în principal asociat cu infecții orale, manifestându-se adesea ca herpes labial. Transmiterea se face prin contact direct cu saliva sau suprafețe contaminate de virus. Deși infecțiile HSV-1 sunt dobândite frecvent în copilărie, adulții pot, de asemenea, să contracteze virusul prin activități cum ar fi sărutul sau partajarea obiectelor personale. După infecția inițială, virusul devine latent în ganglionii nervilor cranieni, având potențialul de a se reactiva și de a provoca leziuni recurente.

HSV-2

HSV-2 este predominant asociat cu infecții genitale și se transmite prin contact sexual. Similar cu HSV-1, HSV-2 poate deveni latent în ganglionii nervoși, în acest caz, în ganglionii sacrali, cu posibilitatea de reactivare sub forma unor leziuni genitale recurente. Infecția cu HSV-2 este un factor de risc semnificativ pentru transmiterea HIV, dat fiind că leziunile genitale pot facilita intrarea virusului HIV în organism.

Diagnosticul serologic

Testele serologice pentru anticorpi IgG specifici HSV pot diferenția între infecțiile cu HSV-1 și HSV-2, oferind informații valoroase pentru managementul clinic. Prezența anticorpilor IgG specifici indică o expunere anterioară sau o infecție cronică activă, în timp ce prezența anticorpilor IgM poate sugera o infecție recentă sau activă. În cazul infecției neonatale sau a encefalitei herpetice, detectarea IgM are o importanță deosebită.

Infecțiile cu virusul herpes simplex (HSV) tip 1 și tip 2 pot avea consecințe serioase asupra fătului atunci când sunt contractate în timpul sarcinii, mai ales dacă infecția este primară. Efectele asupra fătului variază în funcție de momentul sarcinii în care mama contractează virusul și de tipul de virus (HSV-1 sau HSV-2). În continuare, voi detalia efectele potențiale asupra fătului:

Herpes neonatal

Herpesul neonatal reprezintă cea mai gravă manifestare a infecției HSV la nou-născuți, fiind asociat cu o rată înaltă de morbiditate și mortalitate. Acesta poate fi cauzat de oricare din cele două tipuri de HSV, dar HSV-2 este cel mai frecvent implicat în transmiterea verticală de la mamă la făt. Infecția neonatală poate apărea intrapartum, la trecerea fătului prin canalul de naștere infectat, sau poate fi contractată postnatal prin contact direct cu leziuni herpetice sau secreții infectate.

Manifestările herpesului neonatal

  1. Boli diseminate: Aproximativ o treime din cazurile de herpes neonatal se manifestă sub formă diseminată, afectând mai multe organe, inclusiv ficatul, plămânii, creierul și pielea. Aceasta este cea mai severă formă și poate duce la sepsis, icter, hepatosplenomegalie, pneumonie, convulsii și adesea la deces dacă nu este tratată prompt.
  2. Encefalita herpetică: Reprezintă o infecție a creierului și este asociată cu o rată ridicată de morbiditate pe termen lung, incluzând întârzieri de dezvoltare, paralizie cerebrală și tulburări de convulsii. Deși poate fi tratată, encefalita herpetică poate lăsa sechele neurologice permanente.
  3. Boala localizată la piele, ochi și gura (SEM): Este cea mai frecventă formă și implică leziuni cutanate, conjunctivită și, uneori, leziuni orale. Deși această formă este mai puțin severă, tratamentul prompt este crucial pentru a preveni diseminarea infecției.

Prevenirea transmiterii verticale

Prevenirea infecției fătului cu HSV este esențială și include:

  • Testarea gravidelor pentru HSV, în special dacă prezintă semne sau simptome de infecție genitală herpetică.
  • Administrarea de antivirale în ultimele săptămâni de sarcină la femeile cu istoric de infecție genitală herpetică pentru a reduce riscul de recurență și transmitere la naștere.
  • În cazurile de leziuni herpetice active sau suspiciunea de herpes genital primar la momentul nașterii, se recomandă efectuarea unei cezariene pentru a reduce riscul de transmitere a virusului la făt.

Tratament

Pentru nou-născuții diagnosticați cu herpes neonatal, tratamentul cu antivirale, cum ar fi aciclovirul administrat intravenos, trebuie inițiat cât mai curând posibil pentru a reduce severitatea bolii și pentru a preveni complicațiile pe termen lung.

În concluzie, infecția cu HSV în timpul sarcinii necesită o abordare atentă și coordonată între medicii obstetricieni și specialiștii în boli infecțioase pentru a minimiza riscurile pentru făt și pentru a gestiona eficient orice infecție neonatală care poate apărea.